NIS2: scope first, evidence second
NIS2 is EU Directive 2022/2555. Determine applicability and the relevant national implementation before claiming obligations or compliance. Articles 20, 21 and 23 connect governance, risk measures and significant-incident reporting. This original preparation worksheet is not a country-specific legal opinion or a compliance certificate.
SecNet learning series · 1.0 · Source check: 2026-10-11Original SecNet educational content. Examples are fictional; this is not a publication or endorsement by the referenced organizations.
Information security · three objectives
Controls protect different properties of an information asset.
Limit access, protect stored/transmitted data, and review sharing decisions.
Show process diagram
How to plan and execute
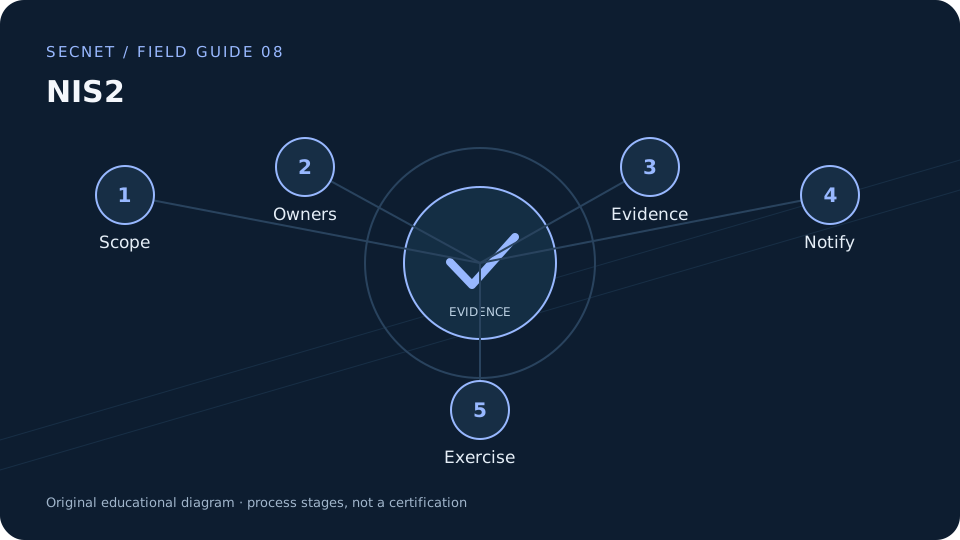
- Identify legal entities, services, sectors, establishment and size; check exceptions and the national competent authority with qualified local advice. Keep scope assumptions dated.
- Assign management oversight, accountable control owners and training records. Put unresolved scope questions on the decision register rather than assuming every supplier is directly in scope.
- Map service dependencies, incident handling, continuity, supply-chain assurance and control effectiveness to existing evidence. Record gaps with owners and due dates.
- Design an incident decision log: awareness time, significance assessment, reporting authority and message owner. Check applicable sector-specific implementing rules and national procedures.
- For significant incidents, Article 23 generally sets early warning within 24 hours, notification within 72 hours and a final report within one month of notification. Trust services and ongoing incidents have specific provisions; confirm the applicable path.
- Run a tabletop using incomplete information, out-of-hours contacts and supplier dependencies. Review evidence, board decisions and notification readiness after the exercise.
Tools & work records
- Scope worksheet — entity/service/country/size, authority, national source and legal review date.
- Control evidence map — reuse controlled risk/incident/continuity records instead of creating a duplicate document warehouse.
- Incident timeline — awareness timestamp and responsible notifier; distinguish NIS2 from separate personal-data breach duties.
What reports are produced?
- Applicability memo with national sources and unresolved questions.
- Risk/control gap assessment and management action plan.
- Incident-notification tabletop report and decision timeline.
Connect the decision to evidence
Fictional logistics provider: a supplier outage interrupts a critical service. The team records when it became aware, evaluates significance under the applicable rules and assigns a notification owner. A preliminary message can distinguish known facts from uncertainty; the exercise measures decision delay without asserting that every outage triggers the same legal duty.
Closure check
- National scope and authority checked?
- Awareness and significance decisions timestamped?
- Management owns evidence-backed corrective actions?
Official sources
Use these sources for criteria, tools and regulations; verify applicability and version for the actual assessment.